

Published on
The OWASP Top 10 is a valuable resource for the AppSec community, as it outlines the most prevalent vulnerabilities that developers must be aware of.
What is an injection attack? An injection attack is a cyberattack in which untrusted input is processed by an application as part of a command or query, so the attacker's data is executed as code. Classic examples include SQL injection, command injection, LDAP injection, and cross-site scripting (XSS), which OWASP now classes as a form of injection.
In this article, we will focus on Injection Attacks and advise how to prevent them in your code. We also recommend The Diligent Developer Chronicles as a helpful training resource for your development team.
Read More About OWASP Top 10: OWASP Top 10 Cryptographic Failures Explained
Key Takeaways
-
An injection attack happens when untrusted input is interpreted by an application as code or commands instead of plain data, letting an attacker read, change, or destroy information or take over the system.
-
Injection is category A03:2021 in the OWASP Top 10, and OWASP merged Cross-Site Scripting (XSS) into the Injection category in the 2021 list.
-
Common injection types include SQL, command (OS), LDAP, XPath, NoSQL, and XSS, each exploiting a different interpreter that mixes input with instructions.
-
The core defenses are parameterized queries (prepared statements), input validation with allow-lists, output encoding, and least-privilege access.
-
Continuous secure-code training, not just annual sessions, keeps developers ahead of injection risks.
What are Injection Attacks?
Injection attacks are a type of cyberattack that involves injecting malicious code into a vulnerable application. The application can then execute this malicious code, giving the attacker control over the application or the underlying system.
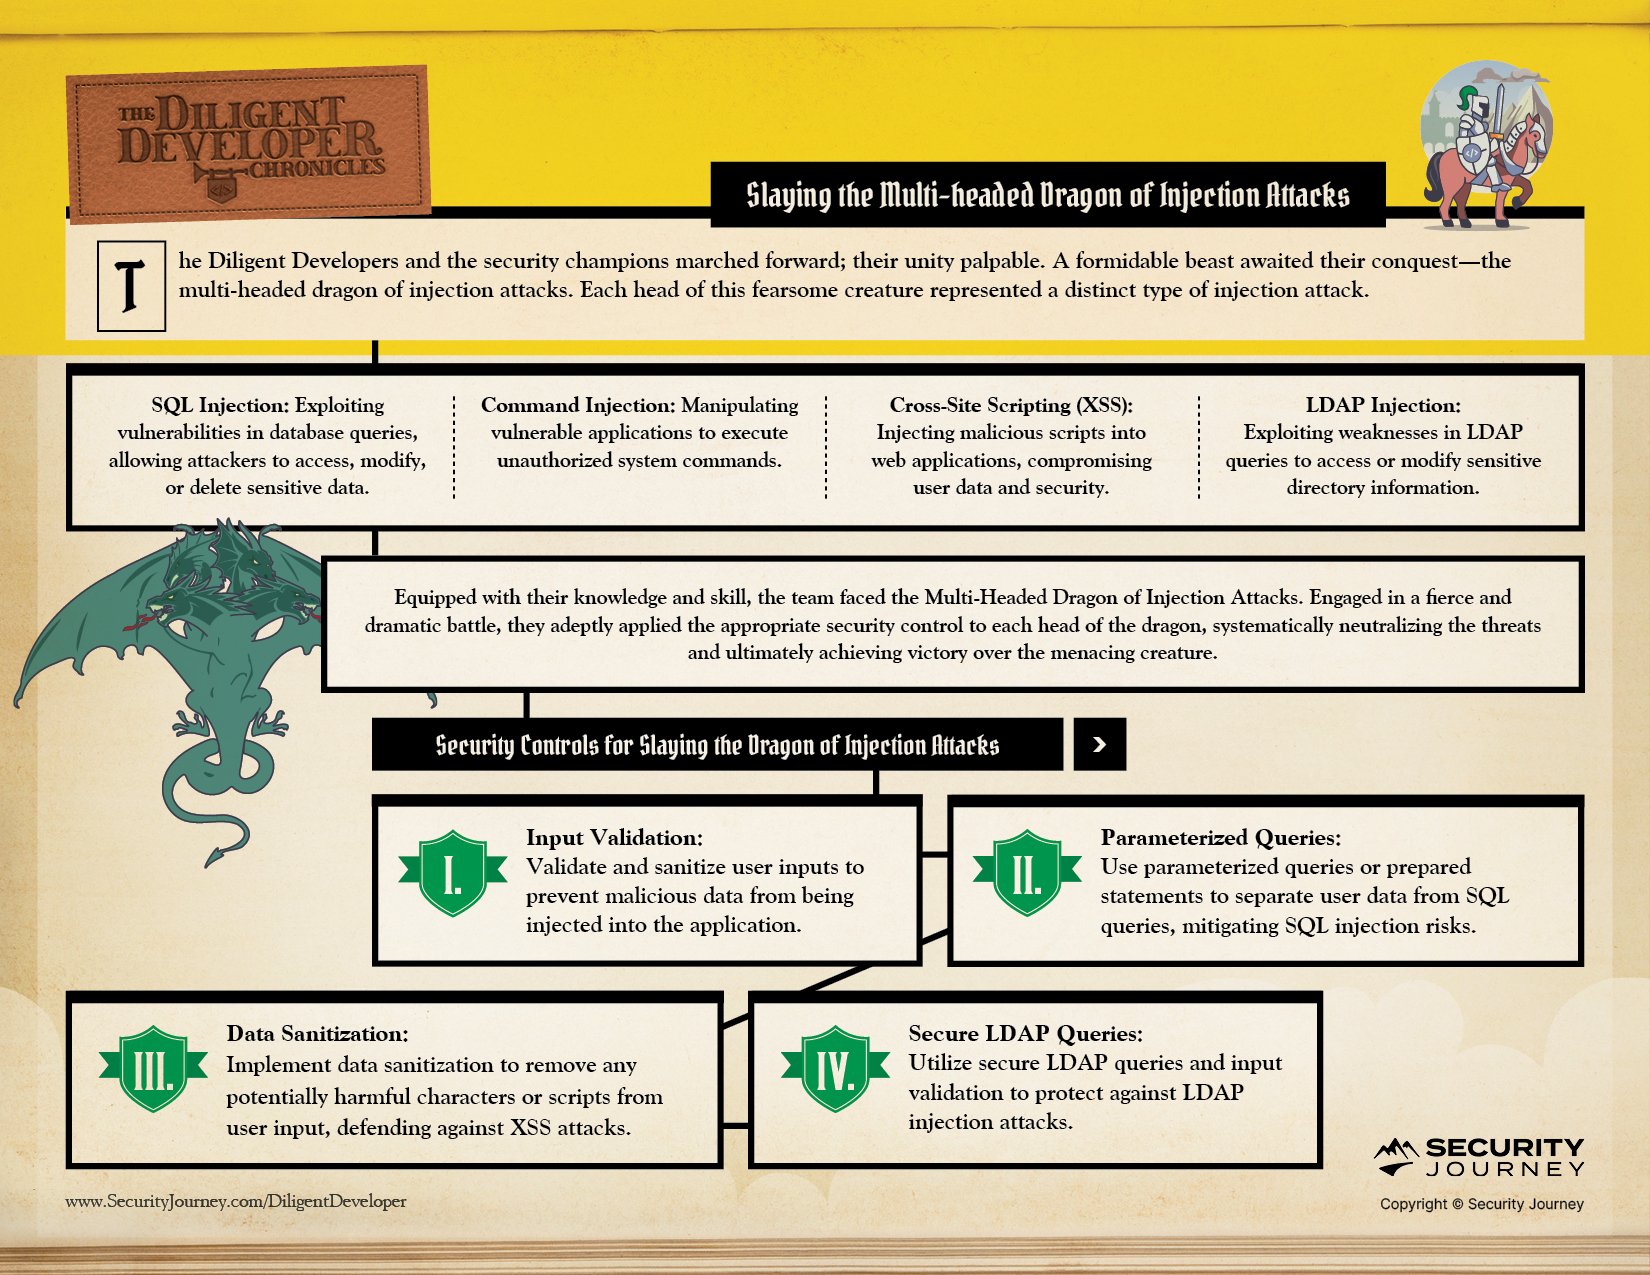
There are four main types of injection attacks to look out for:
SQL Injection
With an SQL injection, a vulnerability that allowed attackers to exploit weaknesses in database queries, granting unauthorized access, manipulation, or deletion of sensitive data
Command Injection
A command injection is a technique enabling attackers to manipulate vulnerable applications into executing unauthorized system commands
Cross-Site Scripting (XSS)
Cross-Site Scripting injects malicious scripts into web applications
LDAP Injection
An LDAP Injection is an exploitation of weaknesses in LDAP queries, which could grant unauthorized access or facilitate unauthorized modification of sensitive directory information
Read More: OWASP: A03:2021 – Injection
Injection types at a glance: how they work and how to prevent them
|
Injection type |
How it works |
How to prevent it |
|
SQL injection |
Untrusted input is concatenated into a SQL query, letting an attacker read, change, or delete database records. |
Use parameterized queries / prepared statements, validate input with allow-lists, and apply least-privilege database accounts. |
|
OS / command injection |
Input is passed to a system shell, so attacker-supplied strings run as operating-system commands. |
Avoid shell calls, use safe APIs with argument arrays, validate against allow-lists, and run with minimal privileges. |
|
Cross-site scripting (XSS) |
Malicious script is injected into a page and executes in other users' browsers. OWASP merged XSS into Injection in 2021. |
Apply context-aware output encoding, validate input, and use a Content Security Policy. |
|
LDAP injection |
Unsanitized input alters an LDAP directory query to bypass authentication or expose directory data. |
Escape LDAP special characters, use secure query construction, and validate input strictly. |
|
XPath injection |
Input is injected into an XPath query against XML data to retrieve unauthorized nodes. |
Use parameterized XPath, validate input, and avoid building queries by string concatenation. |
|
NoSQL injection |
Attacker input manipulates a NoSQL query or operator (for example in MongoDB) to bypass checks or extract data. |
Use typed query builders and ORM safeguards, validate and cast input, and reject query operators from user data. |
Real-Life Example of an Injection Attack: Colonial Pipeline Attack
The Colonial Pipeline Injection Attack was a ransomware attack that took place on May 7, 2021. The attack targeted the Colonial Pipeline, which is a major pipeline that transports gasoline and jet fuel from the Gulf Coast to the East Coast of the United States.
Colonial Pipeline attack involved the injection of malicious code into the company's systems. The malicious code was used to encrypt the data, but it was not used to steal data or disrupt operations. After a week, the company paid the ransom and the attackers released the decryption key.
Read More on Security Boulevard: The Colonial Pipeline Ransomware Attack: Everything We Know
How Can You Protect Against Injection Attacks?
You protect against injection attacks by keeping untrusted input separate from code. The highest-impact controls are parameterized queries (prepared statements), strict input validation with allow-lists, context-aware output encoding, and least-privilege access.
The key to protecting against injection attacks is to validate user input and use parameterized queries. To learn more, check out this guide on input validation for secure coding.
Here are some ways you can prevent Injection Attacks within your code:
Input Validation
By thoroughly validating and sanitizing user inputs could effectively prevent malicious data from infiltrating the application through injection.
Parameterized Queries
Parameterized queries or prepared statements can separate user data from SQL queries, mitigating the risks posed by SQL injection.
Data Sanitization
To combat XSS attacks, Data Sanitization measures enable the elimination of potentially harmful characters or scripts from user input.
Secure LDAP Queries
For protection against LDAP injection attacks, Secure LDAP Queries and meticulous input validation can protect against any attempts to exploit weaknesses in LDAP queries.
Least Privilege and Defense in Depth
Beyond the controls above, run application and database accounts with the least privilege they need, so a successful injection has limited reach. Pair this with web application firewalls and monitoring as defense in depth, and consult the OWASP Injection Prevention Cheat Sheet for language-specific guidance.
Bring The Diligent Developers to Your Organization
Our AppSec experts at Security Journey recommend that developers don’t just take annual training on the most current OWASP Top 10 to be aware of prominent vulnerabilities and code risks but to have continuous training and conversations about code security in your organization.
But why not have fun in the process?
Security Journey developed The Diligent Developer Security Awareness & Education Program as a fun way to not only enhance security awareness, but to build skills across your development team to empower them to think securely. This could be added to National Cybersecurity Awareness month initiatives for the entire development team or be used to engage/grow a security champions program -- whatever works best for your organization.
In Chapter Three, The Diligent Developers take on the Multi-Headed Dragon of Injection Attacks:
As The Diligent Developers continue on their journey, stay tuned to see what OWASP Top 10 Challenge they take on next.
Visit our webpage to learn more about accessing program materials and a program guide to train your organization on OWASP Top 10 vulnerabilities effectively.
Frequently Asked Questions About Injection Attacks
What is an injection attack?
An injection attack is a cyberattack where an application treats untrusted input as part of a command or query, so the attacker's data runs as code. This can expose, alter, or delete data or hand the attacker control of the system. SQL injection, command injection, LDAP injection, and XSS are common examples.
What is the most common type of injection attack?
SQL injection is the most common and widely exploited type. It inserts malicious input into database queries to read, change, or delete records, and it is tracked as CWE-89.
Where does injection rank in the OWASP Top 10?
Injection is category A03:2021 in the OWASP Top 10 (2021). In that edition, OWASP merged Cross-Site Scripting (XSS) into the Injection category.
Is cross-site scripting (XSS) considered an injection attack?
Yes. As of the 2021 OWASP Top 10, XSS is part of the Injection category (A03:2021) because it injects attacker-controlled script that the browser executes.
How do you prevent injection attacks?
Use parameterized queries or prepared statements, validate input against allow-lists, apply context-aware output encoding, and enforce least-privilege access. Together these keep untrusted input from being interpreted as code.
