

See Security Journey Training in Action
Explore training from Secure Code Training and AI Advantage, with interactive lessons designed to build practical skills for developers and all employees organizational-wide.
secure code training
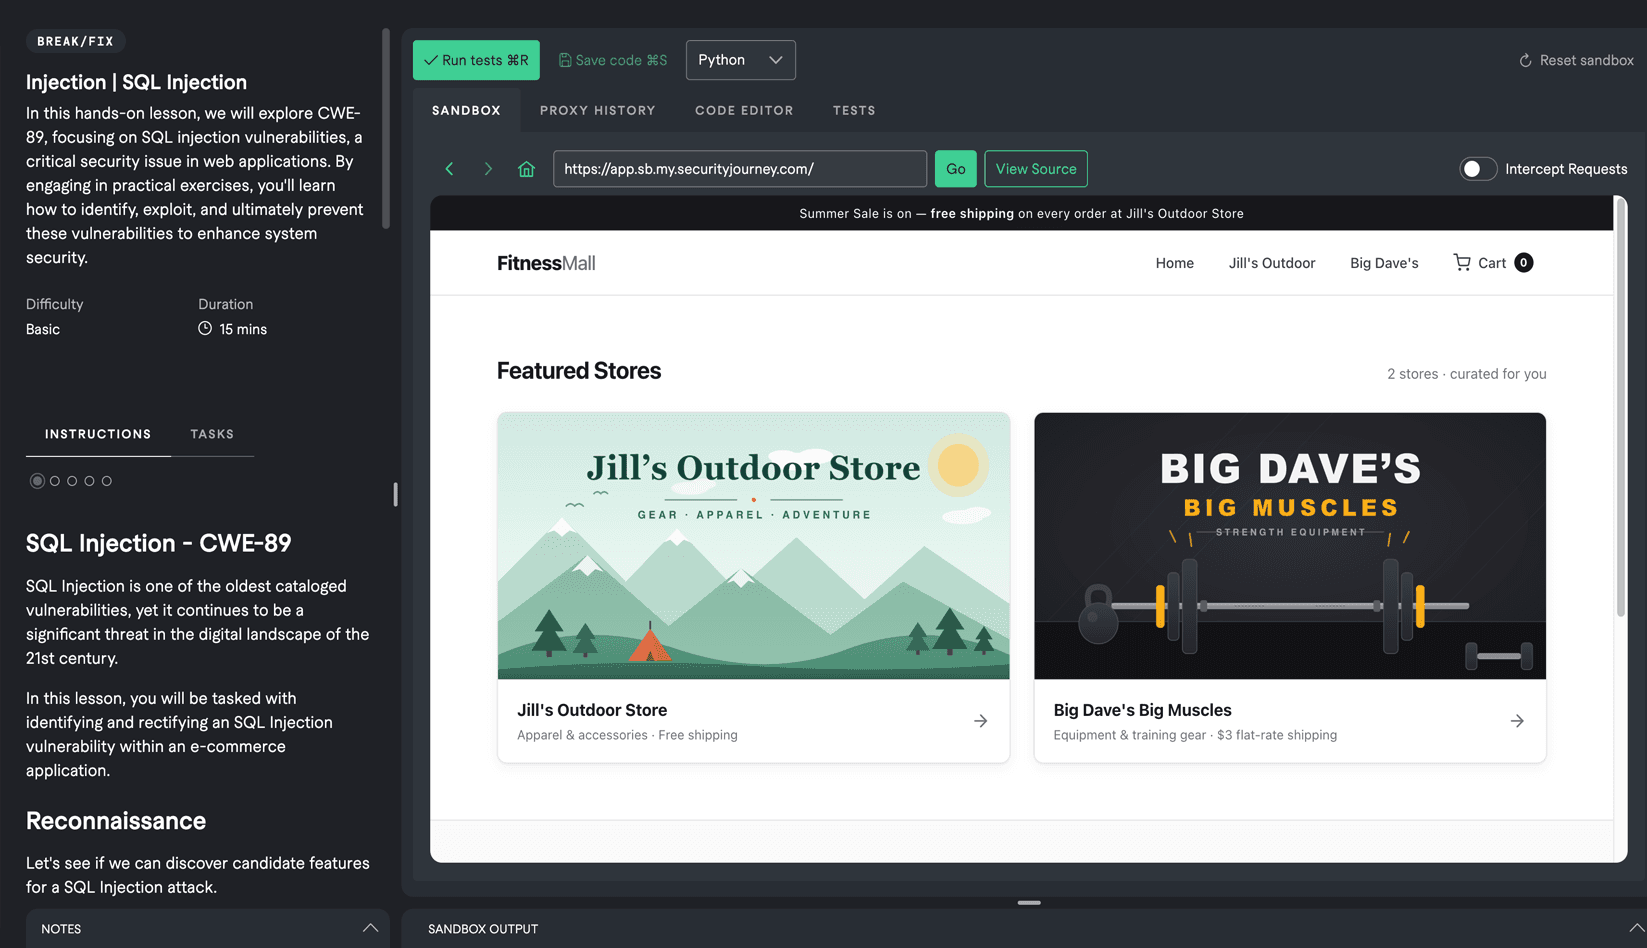
SQL Injection
Explore CWE-89 through hands-on exercises that teach you to identify, exploit, and prevent SQL injection vulnerabilities.
AI Advantage
Prompting (Lab)
Turn prompting into a practical, measurable skill by learning to give AI clearer, more effective instructions. Practice improving prompts and getting feedback.
secure code training
PHP2Shell
In this hands-on lab, you'll take on both attacker and defender roles. First, exploit a vulnerable PHP instance. Then, harden the runtime and its container to limit the blast radius of a successful attack.
secure code training
PHP2Shell Explained
Learn about the PHP2Shell vulnerability and how to patch your PHP instance.
Next Step
Schedule a personalized demo
No pressure. No hard pitch. No catches. Now that you've tried the training, take a guided tour of the Enterprise AI Training & Capability Platform.
- 30 minutes
- See admin reporting, learning paths, assessments
- Straight answers on pricing and rollout
Book your tour
We'll reply within one business day.